English

- Products
Why Enterprises Need White Label Crypto Solutions to Build Web3 Infrastructure
More InfoCentralized Exchange (CEX) Launch in 7 days with enterprise-grade exchange systemsWallet MPC and cold storage for full asset protectionLiquidity Global liquidity aggregation with tight spreadsDecentralized Exchange (DEX) Cross-chain, non-custodial decentralized tradingNFT Platform One-click deployment for multi-mode NFT tradingUser Growth Integrated acquisition and retention operation toolsPrediction Market NewMulti-oracle architecture with on-chain settlementRWA Compliant tokenization for real-world assets - Solutions
- Blog
- About Us


MPC Custody Architecture Guide: Three‑Layer Isolation & Exchange Hack Risk Prevention
Abstract
Asset security remains the top priority for licensed VASP operators in 2026. A large number of security incidents occur on platforms relying on traditional multi‑sig wallets or third‑party custody middleware. MPC multi‑party computation custody has gradually become the mandatory technical standard for mainstream regulated exchanges. Many operators only understand the concept of MPC but lack system‑level implementation experience, leading to hidden risks in key partition, key shard storage and hot‑cold switching logic. This article disassembles the three‑layer isolated MPC custody architecture, sorts typical attack scenarios in actual operation, summarizes audit checkpoints, and explains SoonTech built‑in MPC custody module’s implementation for white‑label exchange deployment.
1. Difference Between MPC and Traditional Multi‑Signature Wallet
Traditional multi‑sig generates complete private keys on‑chain and completes signature verification through multiple addresses. Once enough private key fragments are leaked, assets can be stolen. MPC never generates a complete private key; private key fragments are distributed among multiple independent nodes, and signatures are completed through multi‑party calculation without exposing the full key. For regulated exchanges, this eliminates single‑point failure risk of private‑key leakage, and meets audit traceability requirements of most regulatory authorities such as MiCA, VARA and MAS. However, MPC is not absolute security; unreasonable node deployment, improper fragment storage and misconfigured access rights will still trigger asset risks.
2. Three‑Layer Isolation MPC Wallet Architecture Design for Exchange
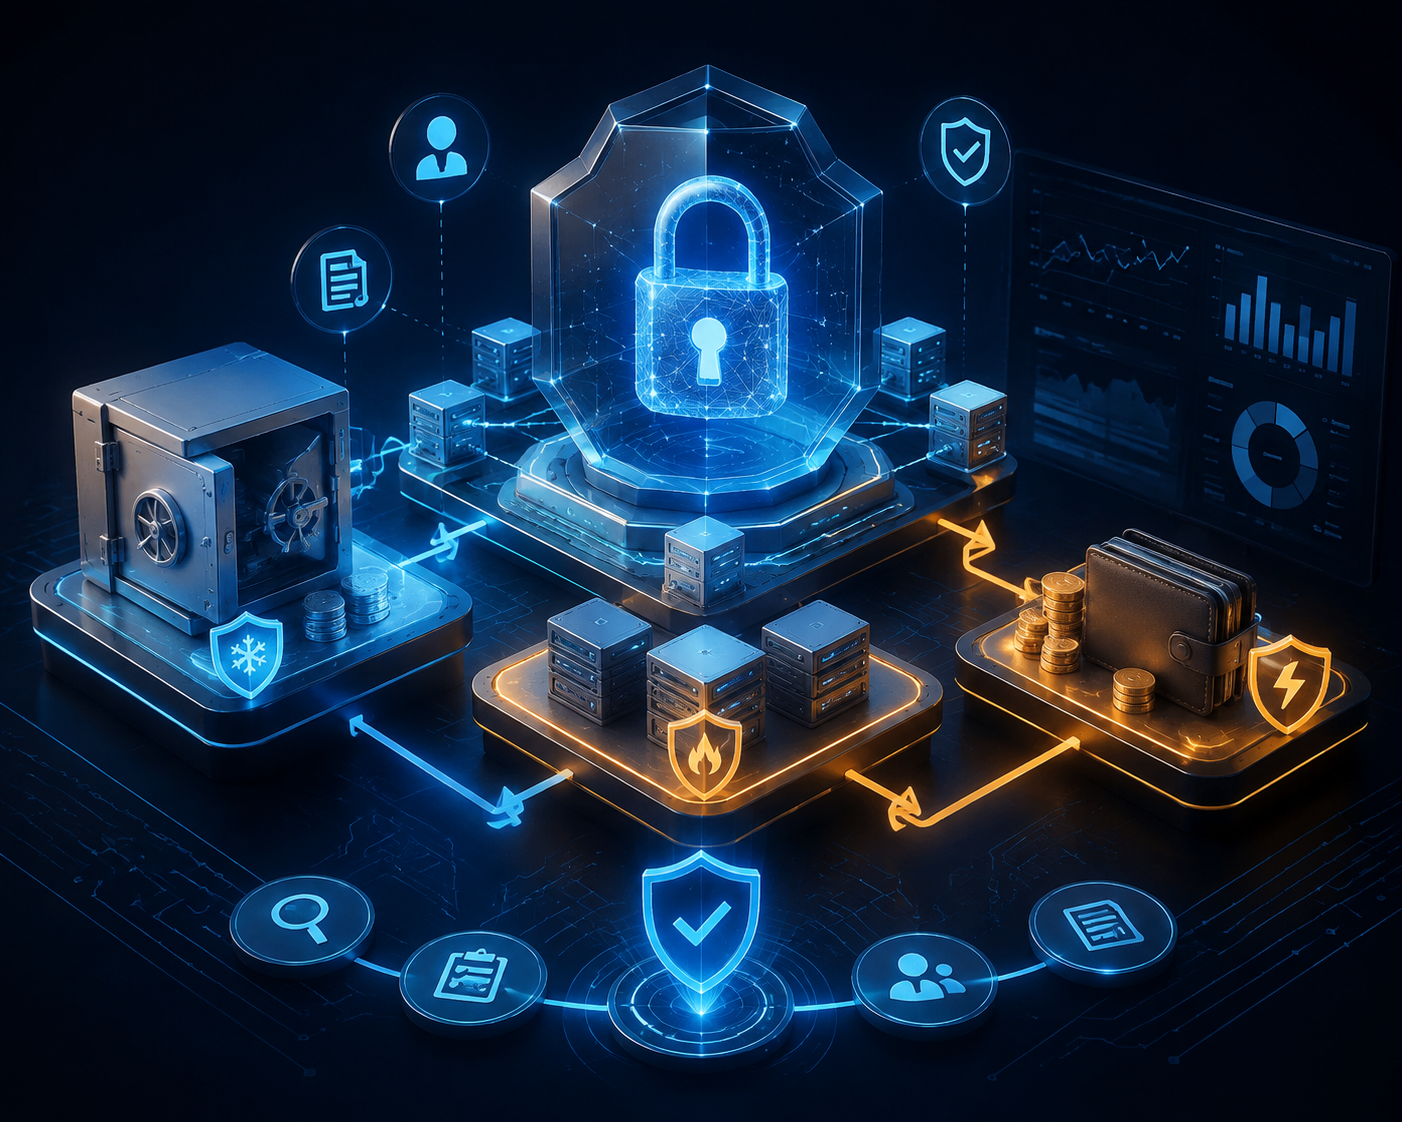
First layer: offline cold storage node. Most user reserve assets are stored on air‑gapped offline MPC nodes. Private key fragments never connect to public network; manual multi‑person authorization is required for asset outflows. Second layer: semi‑warm intermediate node, used for large‑volume fund scheduling between cold wallet and hot wallet, with strict transaction whitelist and quantity threshold restrictions. Third layer: online hot wallet cluster, responsible for daily user withdrawal and deposit matching, only retaining small‑amount operating liquidity. The three layers are logically isolated; cross‑layer fund transfer must pass multi‑administrator review, and all operations leave immutable log records at database and blockchain levels.
3. Typical Attack Risks Under MPC Architecture & Defensive Logic
Common risk points include administrator account hijacking, malicious node intrusion, fragment leakage, replay attacks and abnormal withdrawal storm. Platforms need to build supporting risk‑control systems on top of MPC: IP whitelist for signature nodes, multi‑person quorum mechanism for large‑amount transactions, real‑time on‑chain balance monitoring, automatic withdrawal limit throttling. Many operators mistakenly believe that adopting MPC can ignore business‑layer risk control, which leads to platform losses even if the cryptography itself is secure.
4. Regulatory Requirements for MPC Custody in Major Jurisdictions
Regulators including EU MiCA, UAE VARA, Singapore MAS and Australia ASIC have clear requirements for custody architecture. They require key fragment distribution rules, node deployment location records, administrator permission management records, regular third‑party cryptography audits and emergency asset recovery plans. Pure third‑party outsourcing custody cannot fully meet local audit demands in many jurisdictions; native embedded MPC is easier to adapt to local regulatory log export requirements.
SoonTech Technical Advantages: SoonTech native MPC custody module is deeply coupled with exchange core ledger. Hot‑cold three‑layer isolation is preconfigured. System automatically generates custody audit logs that conform to multiple regulatory formats, supports permission segmentation and quorum signature, and does not rely on external third‑party custody middleware.
5. MPC Deployment & Security Audit Checklist for New Platforms
- Confirm private key fragment distribution quantity and node physical isolation strategy
- Verify large‑value transaction multi‑administrator quorum threshold
- Complete emergency asset recovery drill for node failure
- Penetration test for hot wallet cluster and administrator access interface
- Export complete custody operation log for regulatory inspection
- Regularly execute balance reconciliation between on‑chain assets and system ledger
6. Conclusion
MPC multi‑party computation has become the mainstream custody standard for licensed exchanges, yet security comes from complete architecture rather than cryptography alone. Improper node deployment, permission loopholes and missing business risk‑control will still bring huge hidden dangers. SoonTech’s native embedded MPC three‑layer isolation solution helps new platforms quickly reach the security baseline required by global regulators, avoiding risks caused by secondary development of third‑party middleware.
🌐 Build secure and scalable Web3 platforms with SoonTech.
Explore our solutions for White Label Crypto Exchanges, Prediction Markets, MPC Wallets, Matching Engines, Liquidity Integration, and Compliance.